




Third-Party Risk Management
ComplyScore® Launches World’s First Headless TPRM, Bringing Conversational AI to Compliance Management. 
ComplyScore® Launches World’s First Headless TPRM, Bringing Conversational AI to Compliance Management.

Organizations increasingly rely on third-party vendors, suppliers, and service providers to maximize performance and stimulate growth. Though these third parties bring numerous operational benefits to the organization, they also introduce significant risk. Third-party risks can have severe financial, operational, and reputational impacts, from data breaches to compliance issues. Therefore, managing these risks effectively is crucial for sustainable business operations.
The World Economic Forum's 2026 Global Cybersecurity Outlook found that 65% of large organizations now name third-party and supply chain vulnerabilities as their single greatest barrier to cyber resilience, up from 54% just a year earlier.
A robust third-party risk management (TPRM) framework is essential for identifying, assessing, and mitigating risks associated with external partnerships. It provides a structured approach to evaluating third-party practices, ensuring their alignment with an organization's risk tolerance and regulatory requirements. As cyber threats and regulatory scrutiny continue to evolve, IT leaders must adopt a proactive and comprehensive TPRM strategy to safeguard their assets and maintain compliance.
Let’s explore what TPRM is, its key components, how you can implement it in your organization, and much more.
A third-party risk management framework is a structured approach that helps organizations assess, monitor, and mitigate risks tied to their third-party relationships, including cybersecurity, compliance, financial stability, and operational risk across vendors, suppliers, and partners.
It covers the full lifecycle of a third-party relationship, from onboarding through termination, so risk is visible early enough to act on rather than discovered after it's already affected the business. A comprehensive framework typically includes five stages: risk identification, due diligence, onboarding, monitoring, and offboarding.

Most organizations don't need to design a framework from scratch. Several recognized standards already define how to structure third-party risk oversight, and choosing one gives you a defensible, auditable starting point instead of an internal process no regulator or auditor has seen before.
NIST SP 800-161 is the US federal standard for cybersecurity supply chain risk management. It's built for organizations that work with federal agencies or operate in heavily regulated sectors, and it focuses specifically on supply chain and vendor cyber risk rather than general enterprise risk.
ISO 31000 is a general risk management standard, not TPRM-specific, but widely used as the backbone for enterprise risk programs that include third-party risk as one component. It's a good fit if you're building third-party risk into a broader risk management structure rather than standing it up as a separate function.
ISO 27001 governs information security management and includes supplier relationship controls (Annex A.15), making it a common choice for organizations whose primary third-party concern is data and information security rather than operational or financial risk.
COSO ERM frames third-party risk as one category within enterprise risk management, useful for organizations whose board and audit committee already report against the COSO framework and want TPRM to slot into that existing structure.
The Shared Assessments SIG (Standardized Information Gathering) Questionnaire isn't a full framework but a standardized due diligence questionnaire widely used across TPRM programs to assess vendors consistently, often adopted alongside one of the frameworks above rather than instead of one.
No single framework covers every risk domain. Many programs combine one general framework (ISO 31000 or COSO ERM) for structure with a security-specific standard (NIST 800-161 or ISO 27001) for the cyber and data dimensions, then use a standardized questionnaire like SIG for vendor-facing assessments.
Know your operational limits. Match your framework to risk tolerance for better growth risk balance. A well -matched framework will assist in balancing growth opportunities with risk management.
Different industries are governed by varying regulations regarding third-party risk management. In financial services, for example, the Interagency Guidance on Third-Party Relationships from the Federal Reserve, OCC, and FDIC requires institutions to understand and document risk from critical vendor relationships, not just monitor them informally. Ensure the selected framework is adaptable to meet specific regulatory requirements, including data protection laws, industry-specific compliance standards, and global governance mandates. Staying compliant not only avoids legal penalties but also strengthens market credibility.
Read more about how GDPR and CCPA differ : CCPA vs GDPR
The TPRM framework should seamlessly integrate with your existing systems, including procurement, compliance, and risk management tools. Advanced third-party risk management software can enhance automation, streamline workflows, and provide real-time analytics to support decision-making.
Implementing and maintaining a TPRM framework requires adequate resources, including skilled personnel, budget allocation, and technological tools. Evaluate whether your organization has the necessary resources or needs external support to optimize the framework’s effectiveness.
Organizations where personnel constraints limit program execution often combine a platform with TPRM as a service so framework requirements are met without the program stalling while headcount is approved.
Developing a TPRM framework involves a systematic and strategic approach to ensure comprehensive risk coverage. The process begins by setting clear objectives that align with the organization's risk management strategies.
Clearly define the goals, scope, and expected outcomes of the TPRM framework to align with organizational risk management strategies.
Develop a comprehensive inventory of all third-party relationships, categorizing them by risk level, business impact, and criticality to operations.
Conduct thorough assessments to evaluate potential risks associated with each third party, including financial stability, compliance, and operational risks.
Perform in-depth evaluations of third parties before onboarding, including background checks, compliance status, security protocols, and past performance.
Establish well-defined contracts that include clear risk management clauses, compliance requirements, and terms for risk mitigation strategies.
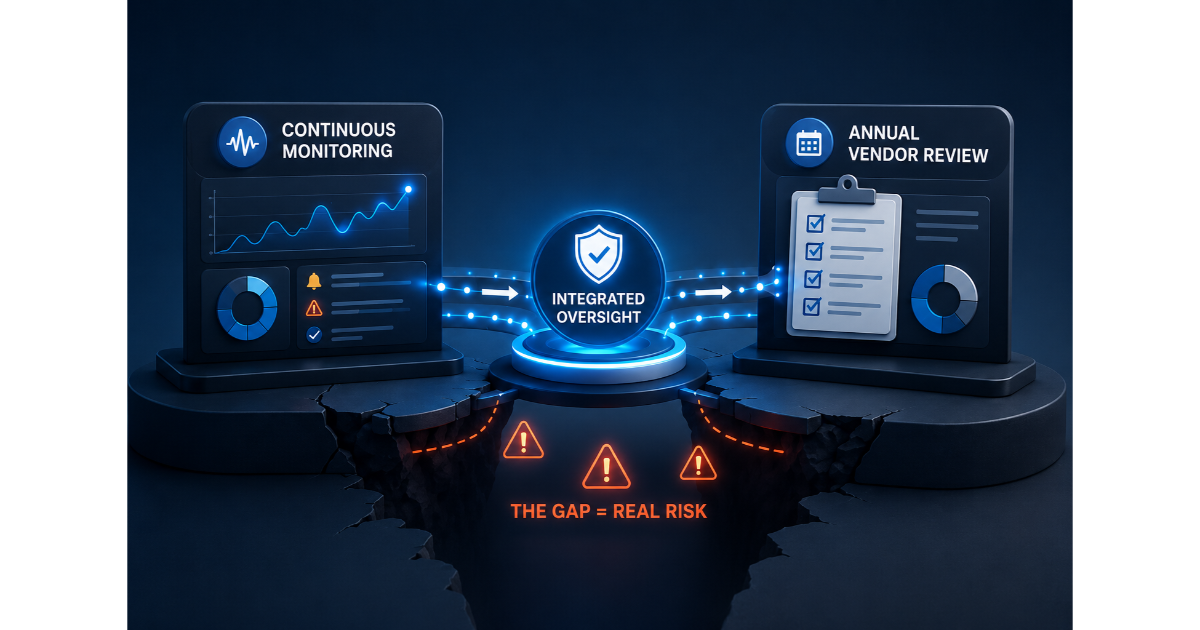
Implement continuous monitoring processes to track third-party performance, compliance, and risk exposure, with regular reporting to stakeholders.
Develop and maintain incident response plans to address potential risk events involving third parties, ensuring swift and effective mitigation.
Regularly review the TPRM framework and update processes to adapt to evolving risks, regulatory changes, and organizational needs.
A robust TPRM framework offers many advantages, enhancing their ability to manage external risks effectively. Implementing a TPRM framework strengthens security and compliance and contributes to overall business resilience. The key benefits include:
A TPRM framework gives you in-depth insights into potential risks associated with third-party vendors. By offering a structured approach to risk assessment, you can identify vulnerabilities early and take proactive measures to address them. Enhanced visibility ensures decision-makers have accurate data to manage risks effectively and maintain operational stability.
TPRM ensures you meet industry-specific regulations and legal requirements, reducing the risk of non-compliance penalties. By implementing robust compliance checks within the TPRM framework, you can align third-party activities with legal mandates, contributing to sustained market credibility and operational security.
You can streamline vendor management processes, optimize resource allocation, and improve overall productivity if you have a TPRM framework in place. It automates repetitive tasks, enhances collaboration across departments, and reduces the time required for vendor onboarding and assessment processes.
It assists in making informed decisions on vendor selection, helping you balance quality and cost-effectiveness. By evaluating third-party risks thoroughly, you can avoid potential losses due to vendor failures or compliance issues, leading to better financial planning and resource management.
It supports resilience by ensuring third-party risks do not disrupt your critical business operations. Through regular monitoring and contingency planning, the TPRM framework prepares you to handle potential disruptions from vendor-related issues, thereby maintaining consistent service delivery and customer satisfaction.
Establishing a robust TPRM framework requires more than setting up policies and procedures. It involves adopting best practices that enhance risk management effectiveness and ensure consistent compliance with regulatory requirements.
An intelligent approach to TPRM includes strategic planning, effective communication, and advanced technologies. From implementing continuous monitoring systems to fostering a risk-aware culture within the organization, these best practices provide the foundation for managing third-party risks proactively and efficiently.
Conduct periodic evaluations of third-party risks to ensure compliance and security measures remain current. This practice helps identify new or evolving risks and allows implementing updated controls to mitigate potential threats effectively.
Prioritize high-risk vendors for closer monitoring based on their impact on critical business functions. This approach enables targeted risk management strategies, optimizing resource allocation and improving overall risk mitigation.
Use third-party risk management software to streamline processes, enhance accuracy, and provide real-time insights. Automation reduces manual effort, increases efficiency, and supports better decision-making through data-driven analytics.
Maintain transparency with third parties about expectations, policies, and compliance requirements. Effective communication fosters trust and collaboration, ensuring third parties adhere to established guidelines and reduce potential risks.
Educate your staff on TPRM processes and risk management strategies to promote a culture of risk awareness. Regular training sessions help the right employees understand their roles in managing third-party risks and reinforce organizational compliance practices.
Implementing a third-party risk management framework involves many stakeholders, evolving regulatory requirements, and integrating advanced technologies. Despite its importance, organizations often encounter significant hurdles during implementation. These challenges can hinder the framework's effectiveness and expose businesses to unmanaged risks that could have been mitigated.
A well-designed TPRM framework requires adequate resources, a deep understanding of regulatory landscapes, and seamless integration with existing systems.
Below are some of the most common challenges faced when implementing a TPRM framework and strategies to address them effectively.
Implementing a TPRM framework requires sufficient financial and human resources. However, many organizations struggle with budget limitations and lack dedicated staff for risk management tasks. This can result in an over-reliance on manual processes, increasing the risk of human error and inefficiency.
To address this, prioritize resource allocation for TPRM initiatives, explore automation through third-party risk management software, and consider outsourcing specific tasks to managed service providers to fill resource gaps effectively.
Managing large volumes of third-party data can be daunting, especially when dealing with diverse data sources and formats. Organizations often face challenges in collecting, organizing, and analyzing vendor data to assess risks accurately. Poor data management can lead to gaps in risk assessments and hinder decision-making.
Implementing robust data management practices, including centralized data repositories and advanced analytics tools, can streamline data processes and improve the accuracy of risk assessments. Automated data collection and integration with risk management platforms can further enhance efficiency.
Some third-party vendors may not comply with the organization's risk assessment processes, either due to a lack of understanding, limited resources, or concerns about sharing sensitive information. This resistance can create blind spots in the risk management process and limit the organization's ability to assess risks effectively.
To overcome this challenge, establish clear communication channels, outline the benefits of compliance to vendors, and consider incentives for cooperation. Building strong partnerships and providing guidance on risk management expectations can also improve vendor collaboration.
The regulatory environment surrounding third-party risk management is constantly evolving, with new standards and compliance requirements emerging regularly. Organizations must stay updated with these changes to avoid regulatory breaches and associated penalties.
Navigating this complexity requires dedicated compliance teams and robust frameworks to adapt quickly to new regulations. Using compliance management tools, automating regulatory monitoring, and participating in industry forums can help you stay informed and maintain compliance effectively.
Integrating a new TPRM framework with existing systems, such as procurement, finance, and IT infrastructure, can be challenging. Disparate systems and outdated technologies may not support seamless data exchange, leading to inefficiencies and potential data silos. Integration challenges can also limit the visibility of third-party risks across the organization.
To mitigate these issues, invest in integration-friendly third-party risk management software that supports API connections and data synchronization. Also, conducting thorough system assessments before implementation can help identify potential integration challenges early on.
ComplyScore® by Atlas Systems provides a robust and customized solution for third-party risk management, proactively reducing potential threats and maximizing the value of vendor relationships. Powered by advanced AI and backed by industry experts, our solution creates a comprehensive risk profile for each vendor, identifying vulnerabilities and potential risks to ensure your business remains strong, secure, and prepared for the future.
Get started with a demo today.
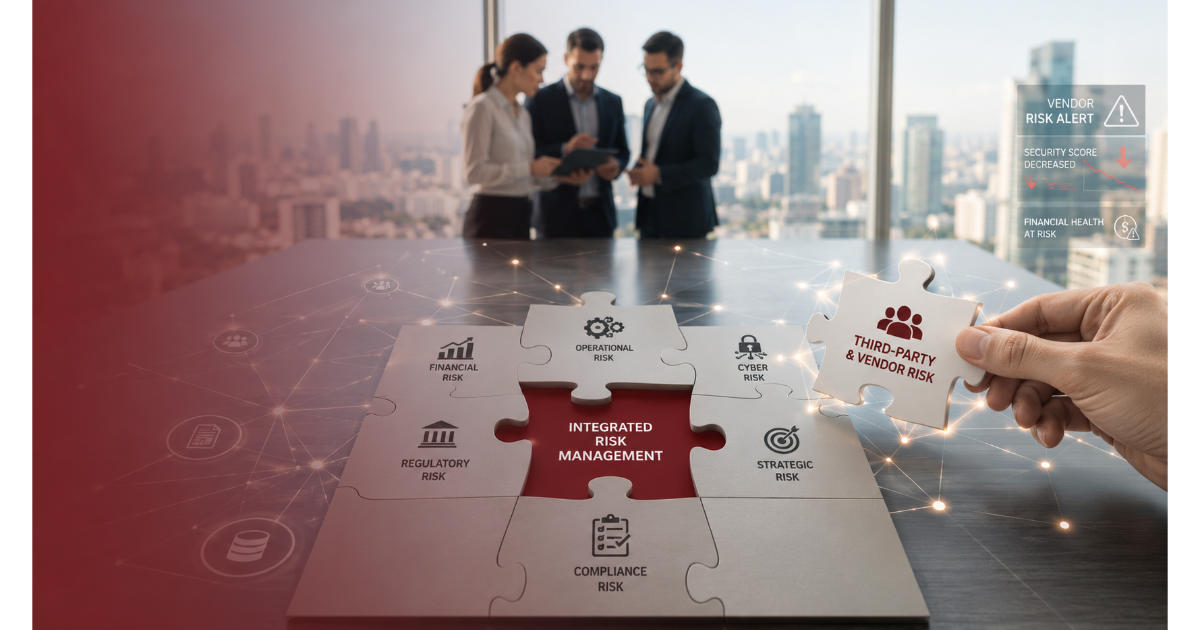
As companies increasingly rely on external parties for services, technology, and supply chains, they expose themselves to risks such as data breaches, compliance violations, operational disruptions, and reputational damage. A robust TPRM framework ensures that third-party relationships are continuously monitored and risks are proactively identified, assessed, and managed.
Many industries, including finance, healthcare, and technology, are subject to strict regulations that mandate risk management practices for third-party relationships. Regulations such as GDPR, CCPA, HIPAA, and frameworks like ISO 27001 and NIST require organizations to assess their vendors' security and compliance posture. Non-compliance with these regulations can lead to fines, legal issues, and reputational harm. Therefore, business leaders must align their TPRM processes with relevant regulations, ensuring due diligence, ongoing monitoring, and thorough documentation of vendor risk assessments.
Common frameworks include NIST SP 800-161 for supply chain cybersecurity, ISO 31000 for general enterprise risk, ISO 27001 for information security controls, COSO ERM for enterprise risk reporting, and the Shared Assessments SIG questionnaire for standardized vendor due diligence. Most programs combine more than one.
A framework is the structure and standards you follow, such as NIST or ISO 31000. A program is how your organization actually runs that framework day to day: the team, tools, policies, and cadence used to identify, assess, and monitor vendors.